 AWS
 Azure
 Google Cloud
In one sentence: a NAT gateway bills every byte it processes, so heavy traffic from private workloads to storage and registries belongs on a private path, not on the default route.
Symptom
The NAT gateway's processed bytes grow with deploys, scale-outs and nightly jobs, not with user traffic. The network share of the bill rises while compute stays flat, and most of the bytes go to object storage, container registries and package mirrors.
How it happens
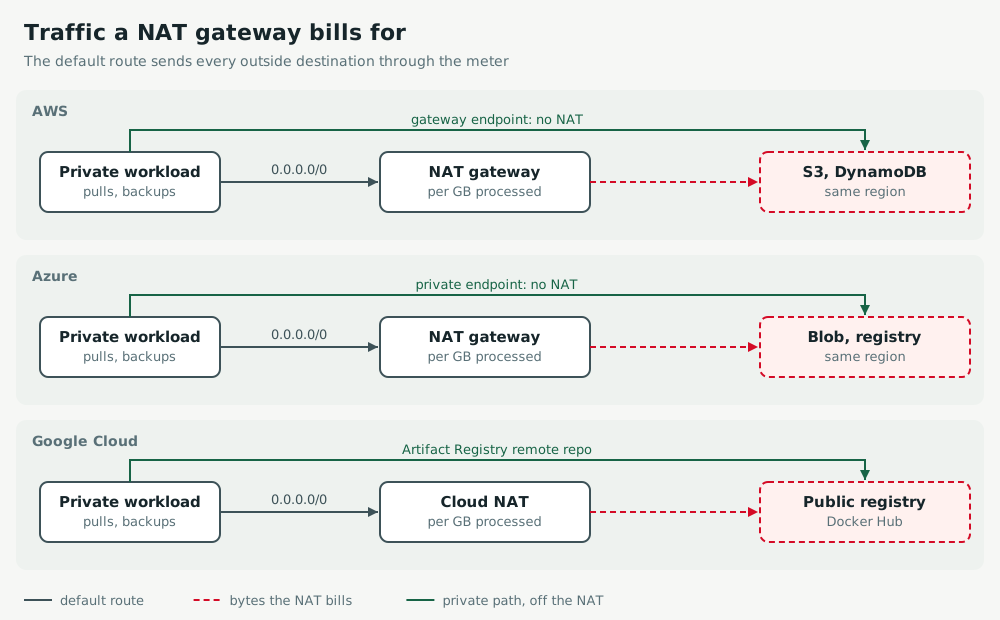
- Private subnets have one default route, and it points at the NAT gateway. Every destination outside the network leaves through it and is metered per byte, unless a private path to that service exists.
- Image pulls, package installs at boot, backups to object storage and log shipping are the heavy flows. Autoscaling multiplies them.
- A private path to the provider's services, or a pull-through cache for public registries, takes those bytes off the NAT.
Act
AWS
Add gateway endpoints for S3 and DynamoDB to every private route table: they carry no hourly or data charge. ECR needs interface endpoints for ecr.api and ecr.dkr (layers come from S3, which the gateway endpoint covers); interface endpoints are billed per hour and per GB, so add them where the volume justifies it. Route each subnet to the NAT gateway in its own Availability Zone.
aws ec2 create-vpc-endpoint --vpc-id vpc-0abc --vpc-endpoint-type Gateway \
  --service-name com.amazonaws.eu-west-1.s3 --route-table-ids rtb-0priv1 rtb-0priv2
Azure
Give storage a private path: a private endpoint for the blob sub-resource, with the privatelink.blob.core.windows.net zone linked to the VNet, or a Microsoft.Storage service endpoint on the subnet. Do the same for Container Registry, whose private endpoints need the Premium tier.
az network private-endpoint create -g rg-app -n pe-blob --vnet-name vnet-app --subnet snet-pe \
  --private-connection-resource-id "$STORAGE_ID" --group-id blob --connection-name blob
Google Cloud
Traffic to Google APIs skips Cloud NAT when Private Google Access is on; Google Cloud enables it on the ranges a NAT gateway serves, but check every subnet. The heavy flows left are public registries and mirrors: serve them from an Artifact Registry remote repository.
gcloud compute networks subnets describe app-subnet --region=europe-west1 \
  --format="value(privateIpGoogleAccess)"
gcloud artifacts repositories create dockerhub --location=europe-west1 \
  --repository-format=docker --mode=remote-repository --remote-docker-repo=DOCKER-HUB
Keep watch
AWS
Alarm on the NAT gateway's BytesOutToDestination and BytesInFromDestination: both directions are processed. VPC Flow Logs on its network interface name the top destinations, and the NatGateway-Bytes usage type in Cost Explorer should drop.
Azure
Alert on the NAT gateway's Bytes metric split by direction. In the storage account's StorageBlobLogs, CallerIpAddress should now be a private address of the VNet.
Google Cloud
Alert on router.googleapis.com/nat/sent_bytes_count and received_bytes_count. Turn on Cloud NAT logging to list top destinations, and confirm image pulls now go to the dockerhub repository.
Exercise
Restore the private paths yourself: Private workloads reach nothing they depend on, then Outbound traffic reaches nothing.